Atlassian Cloud for Regulated Industries
Atlassian Cloud and AI That Pass the Audit
We make data location, access and Rovo agents provable, so security, privacy and your auditors can sign off.
Compliance overview
Rule, control and status at a glance
- GDPRData stays in the EU regionMet
- NIS2Audit log streams to the SIEMMet
- EU AI ActRovo only for approved groupsIn reviewMet
- CADASet the sovereignty tierWatching
Why Governance Can't Wait
GDPR
NIS2
Cyber Resilience Act
Three rulebooks, three different answers to the same question
NIS2 still not in national lawAs of July 2026 – the deadline was October 2024
EU Regulation
Many Rulebooks, Different Deadlines, One Audit
According to the Business Software Alliance, the EU passed some 22 tech laws in 2019–2024 alone. They were written in parallel, so they overlap and sometimes conflict. A single security incident can trigger several reporting duties, each with its own definition, deadline and form.
- NIS2 was due in national law by October 2024. As of July 2026, France, Spain, Ireland and the Netherlands still had none.
- GDPR, NIS2 and the Cyber Resilience Act each define a reportable incident differently.
- National cloud schemes such as Germany's BSI C5 or France's SecNumCloud add their own requirements, some of them about who owns the vendor.
- The EU AI Act is expected to land as broadly as GDPR did, with fines on a similar scale.
What that means for you: your governance has to absorb new obligations without a fresh plan each time. That is how we set up Atlassian Cloud.
Atlassian Platform · As of October 2026
What the Platform Does Today, and What's Coming
Available today
Data in the EU
Tenant isolation
Finding sensitive data
AI agents
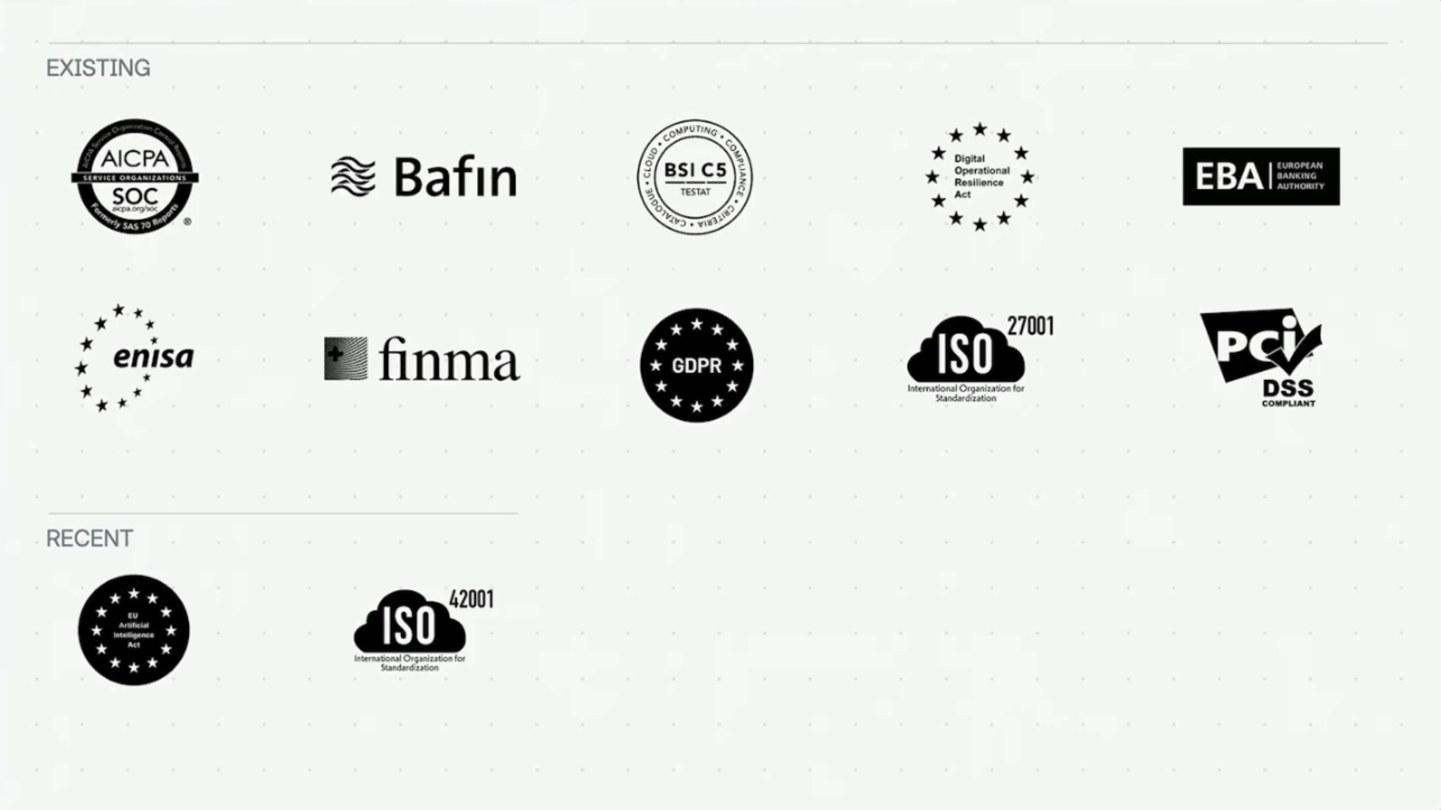
Certifications
Announced or on the roadmap
Data in the EU
Tenant isolation
Finding sensitive data
AI agents
Certifications
 Atlassian Team '26 Europe
How We Work
Four Steps to AI Governance That Grows With You
We work in the loop Atlassian itself recommends: prepare, draw the boundary, monitor, and tighten after every stage of rollout.
Get Your Data AI-Ready
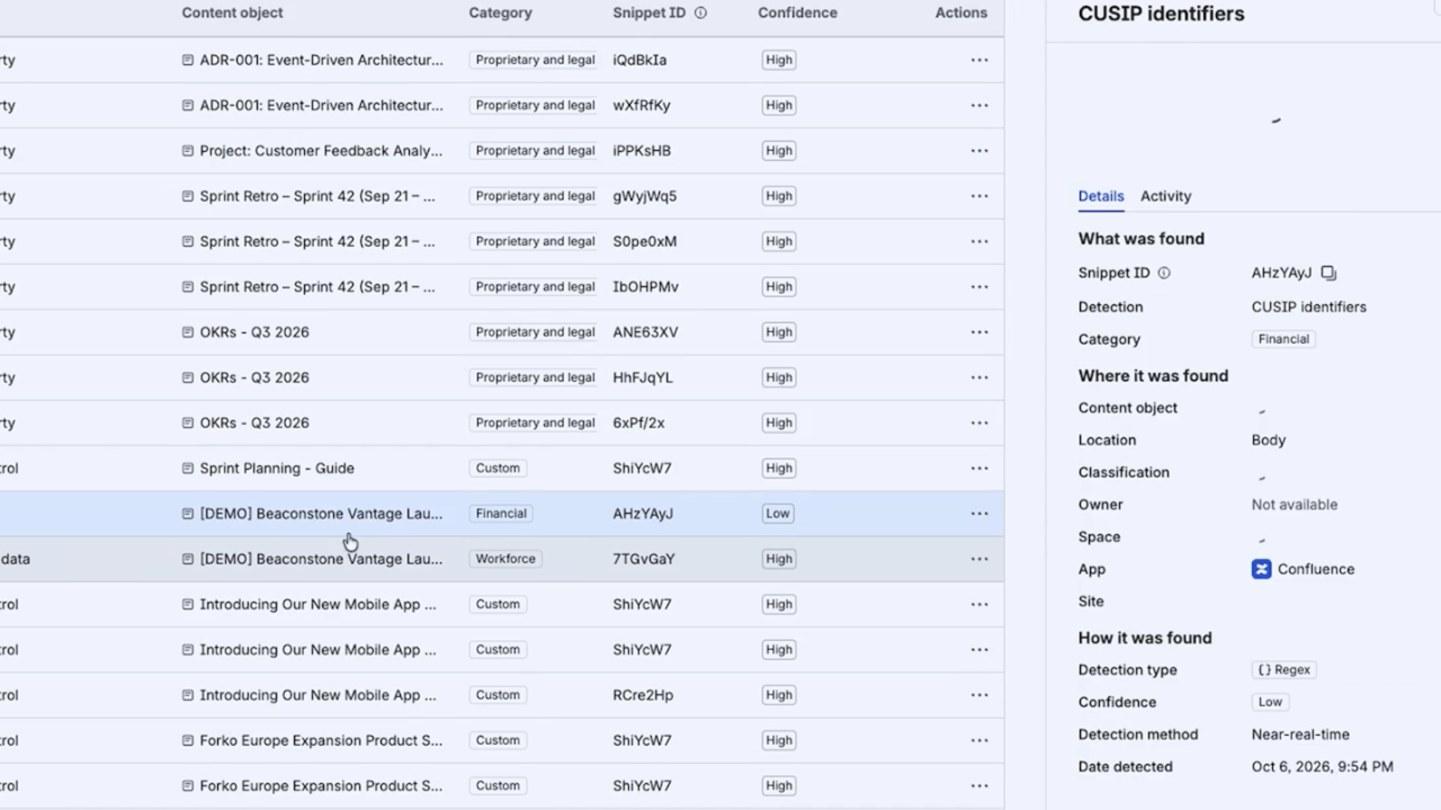
Together we define what counts as confidential, scan the whole site and let policies redact or flag what they find.
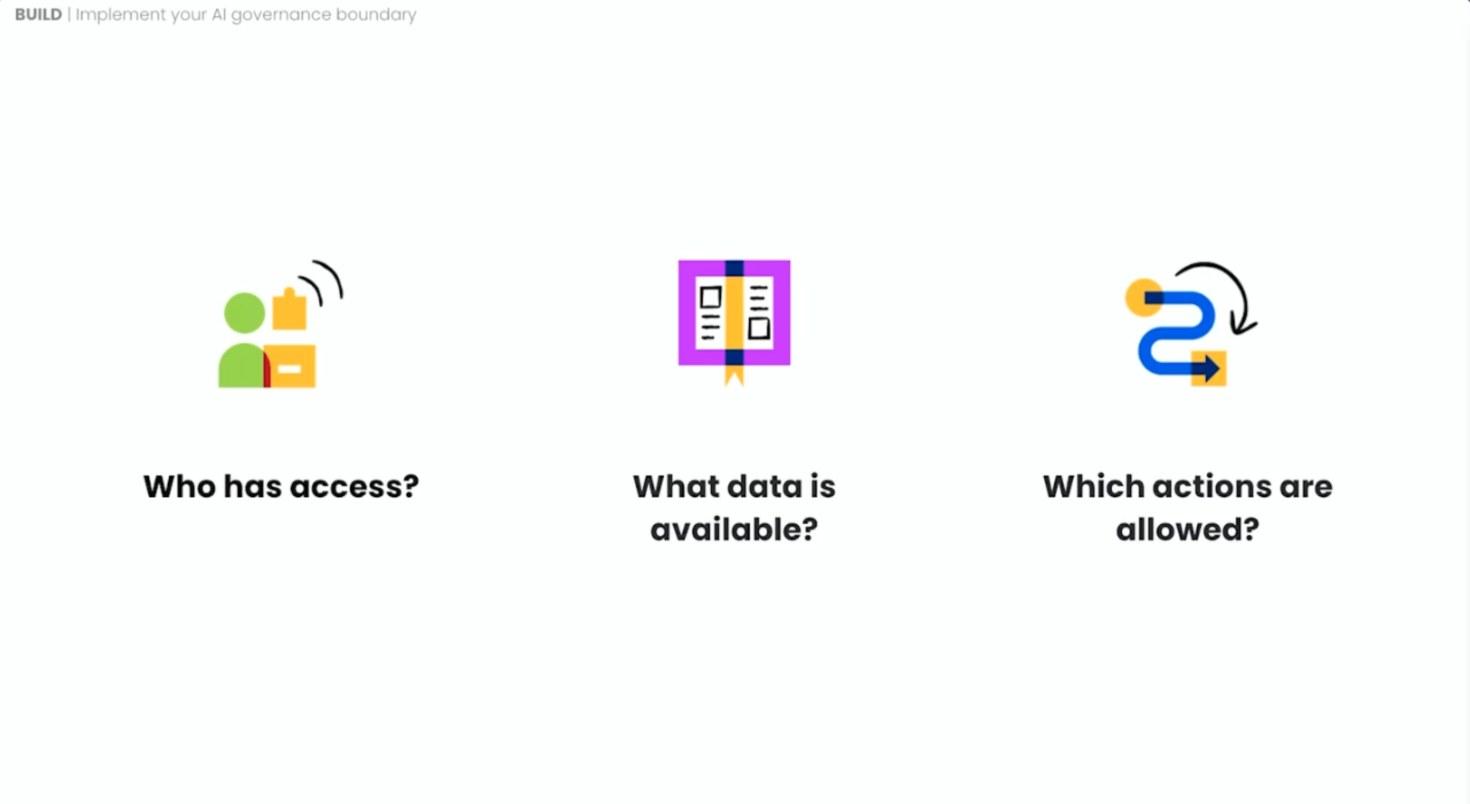
Draw the Boundary
We settle three questions: who has access, what data the AI can see, and which actions an agent may take.
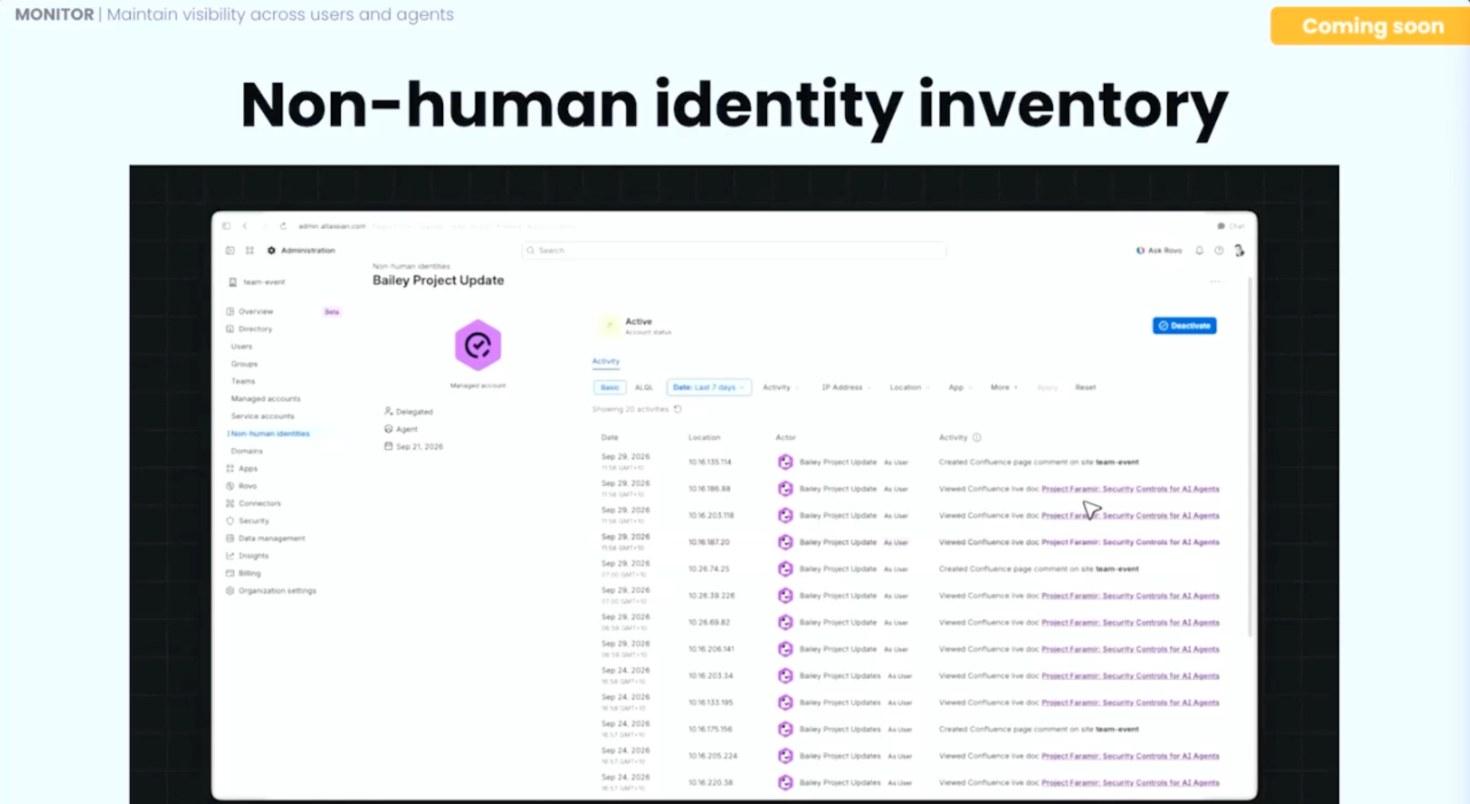
Keep Sight of People and Agents
An overview, an agent inventory and an audit log show who ran which agent, when, and with what tools.
Tighten and Repeat
New features and new obligations move the boundary, so the loop starts again after every stage of rollout.
 Atlassian Team '26 Europe / TeamViewer
Case in Point
TeamViewer Rolls Out Rovo in Stages
TeamViewer switched Rovo on in stages: search first, then chat, then agents. It started with the questions stakeholders were asking about security, privacy and responsible AI, and only widened access once those had answers.
- Due diligence through the Atlassian Trust Center gave the security review a structured starting point.
- Rovo went out by group rather than organisation-wide, so access could grow deliberately, one step at a time.
- Every space got a clear owner and permission upkeep became an ongoing job. Historic permissions were deliberately not all fixed up front.
- In third-level support, Rovo analysed ticket samples. People still did the interpreting and made the call.
Monthly active Rovo users grew roughly eightfold in the early rollout. Toni Soldat is clear that this is not yet proof of business value. Next on TeamViewer's list: the agent lifecycle and data protection.
Features in Detail
What Governance Looks Like in Atlassian
The building blocks we work with, from finding sensitive data to the agent inventory.
Common Questions About Cloud Governance
What IT, security and privacy leads should settle before the next step.
Is data residency enough for digital sovereignty?
For many requirements, no. Data residency governs where data is stored. In its strictest tier, the planned Cloud and AI Development Act (CADA) could also require European capital and European staff. Atlassian says the text is not settled yet, so plan with options rather than one fixed assumption.
Is Isolated Cloud the answer?
For some organisations, yes: Isolated Cloud provides a dedicated, isolated environment. It does not automatically meet data sovereignty requirements, however. Check separately where data resides, which jurisdictions and access rules apply, and whether your specific security requirements are met. The dedicated environment also costs more than the regular cloud.
What does the EU AI Act change for how we use Atlassian?
It is risk-based and, since ChatGPT, has its own rules for AI models. The part people overlook is the AI literacy obligation for your staff. Training belongs in your governance just as much as the technical settings do.
Do we have to clean up every permission before Rovo?
TeamViewer didn't. The team controlled access by group, gave every space an owner and made permission upkeep an ongoing task. A permission check up front shows you where the real risk sits and what can safely wait.
Where should we start?
With three quick steps Atlassian also recommends: use the Trust Center for due diligence, set up custom detections for your sensitive terms, and open agent insights in Atlassian Administration. Add one question: what does sovereignty mean for you in practice? We work that out with you in the governance check.
How We Help
As an Atlassian Platinum Partner, we put the platform's governance building blocks to work in your organisation, from the first scan to policies that actually enforce.
Guard Premium and Classification
We turn your classification scheme into Guard policies and switch them on in stages: watch first, automate second.
Check Permissions Before Rovo
The permission assessment shows which spaces and projects are too open before an AI starts reading them.
Migration With Governance Built In
For teams moving from Data Center to Cloud: we plan data residency, admin structure and policies as part of the move.
Roll Out Rovo and Agents
Group-by-group enablement, agent accounts with least privilege, and an audit log your security team can actually use.
Bring Your Audit Questions
In a first call we work out which of the announced features already cover your requirements, and where you need a bridge until the rest arrives.